Intelligent Migration & Digital Transformation Platform
A technology platform designed to simplify, govern and accelerate Active Directory, Microsoft Entra ID and Microsoft 365 migration programmes.
Get In Touch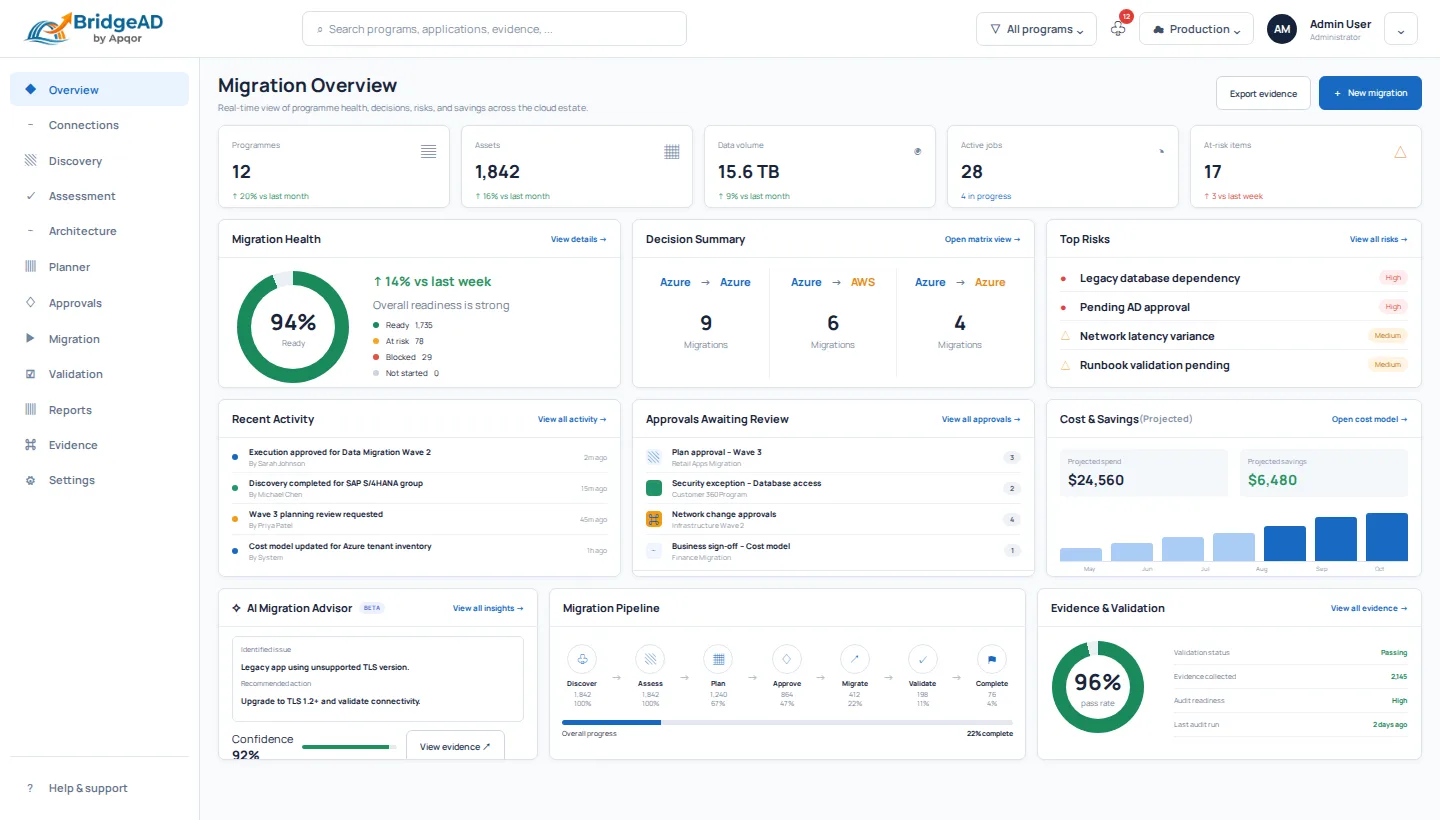
Cloud decisions
Assessment, target design, plan and evidence
Microsoft workloads
AD, Entra ID, Exchange, SharePoint and Teams - plus any-to-any mailbox routes
Migration intelligence
Cited answers, failures and reports
Governed delivery
Approvals, validation and audit evidence
From connection selection to signed-off evidence.
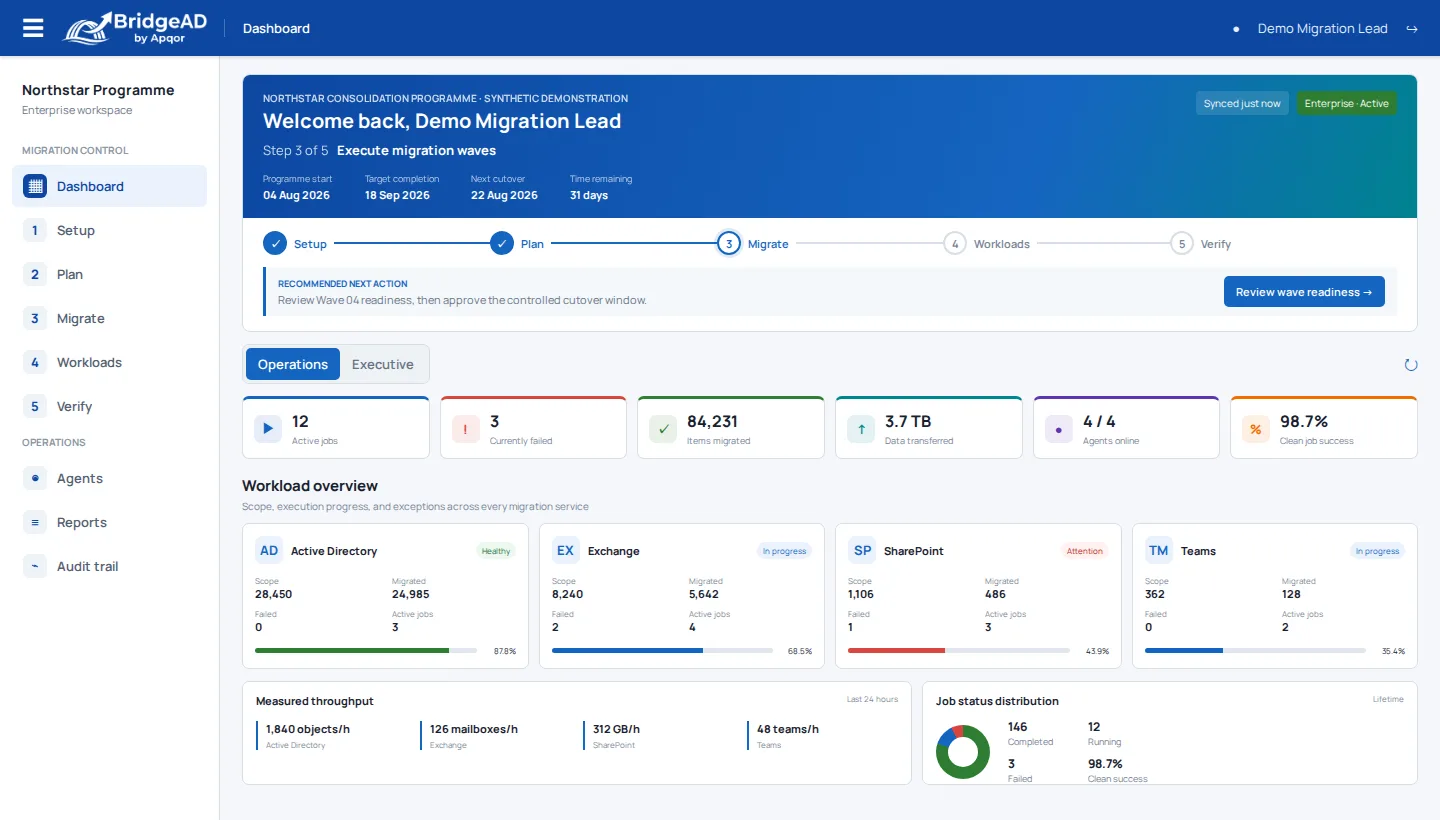
BridgeAD is not only a capability catalog. Operators work through named source and destination connections. They preview changes, start bounded jobs, and watch individual items move. They can intervene safely and close each wave with inspectable outputs.
Select
Choose validated source and destination connections, agents, assessed objects, users, sites, mailboxes, or servers.
Preview
Run dry-run or readiness checks, inspect collisions and unsupported items, then revise mappings or scope before writes begin.
Start
Launch a job, wave, cloud-directory run, endpoint conversion, or server operation with the options attached to that run.
Control
See the current item, processed and failed counts, warnings, throughput, and live state; pause, cancel, resume, or retry where supported.
Prove
Review exceptions and validation, record acceptance, and export reports, certificates, transcripts, and audit evidence.
Start with the migration you actually need to control.
BridgeAD is designed first for AD-heavy and hybrid programs. In these programs, dependencies, operator control, rollback planning, and evidence matter as much as moving objects.
AD forest consolidation
Discover, map, dry-run, and migrate directory objects through controlled waves.
M&A and divestitures
Coordinate identity scope, approvals, execution, and evidence across environments.
Tenant-to-tenant planning
Assess identity and workload readiness before committing to content- transfer scope.
Regulated self-hosted delivery
Keep the control plane in customer-managed infrastructure with explicit cloud egress.
MSP migration delivery
Standardize assessment, pilot boundaries, operator roles, and evidence across client programs.
Two focused products for different migration responsibilities.
Choose Cloud Workloads for AD and Microsoft 365 migration. Choose Intelligence for cloud assessment, planning, controlled execution, analysis, and reporting.
BridgeAD Cloud Workloads
Assess, scope, execute, reconcile, and prove Active Directory, Entra ID, Exchange, sharePoint, OneDrive, and Teams migrations - plus any-to-any mailbox moves across Gmail, IMAR on-premises Exchange, and archives.
BridgeAD Intelligence
Assess cloud estates, compare target designs, verify plans, govern execution, investigate failures, and prepare cited reports.
Dedicated engines for identity and Microsoft 365.
Active Directory
Supported discovery, mapping, CSV workflows, collision checks, and dry runs. Topology-specific controlled pilots then cover execution, delta, SID, ACL, password, and rollback workflows.
Mailbox migration - any to any
Certified routes between Exchange Online tenants, Gmail, IMAP hosts, on-premises Exchange (EWS), and PST/EML archives - mail, owned calendars, contacts, and tasks with resumable delta passes, signed fidelity contracts, and offline-verifiable custody evidence.
SharePoint & OneDrive
Assessment-backed site and drive scoping with resumable Graph content transfer. Conflict handling and version depth are configurable. Permissions are mapped, lists are supported, and delta passes end in reconciliation.
Microsoft Teams
Graph reconstruction for team and channel structure, mapped membership, supported settings, tabs, and tags. Microsoft-native channel-message import is conditional.
Microsoft Entra ID
Graph-based users, groups, devices, and memberships with collision protection. Adds governed guest invitations, selected application definitions, and conditional Intune policy definitions.
Audit & Compliance
Supported audit logging with hash-chain verification, correlation IDs, role-change traceability, and exportable operational reports.
Know what can enter scope before the project starts.
Status applies to the exact scope stated below. Every engagement still depends on tenant state, permissions, connectivity, and identity mappings. Service limits, validation, and owned remediation also apply.
| Capability | Status | Current/Delivery boundary |
|---|---|---|
| AD discovery, mapping, CSV validation, and dry run | Supported | Available for orchestrating when connections and permissions validate. |
| AD migration orchestration and rollback | Supported | Dry-run first with success criteria; per-step rollback, automated rollback rules, and connectivity circuit breakers are built in. |
| SID history and ACL remapping | Supported | Agent-executed with streamed progress and evidence; multi-forest translation follows applied sync and one mapped peer link. |
| Entra users, groups, devices, and memberships | Supported | Configured Graph permissions required; synchronized attributes remain owned by Entra Connect or Cloud Sync. |
| Entra tenant-to-tenant users and static groups | Supported | Preview-first route with UPN transformation, optional update-existing reruns, and membership reconciliation; licenses, mailboxes, and MFA registration remain separate. |
| Google Workspace directory to Entra or AD | Supported | Users and groups only through domain-wide delegation; Gmail, Drive, Calendar, and source passwords are excluded from rollout. |
| Cloud-native device conversion | Supported | AD unjoin, Entra join, Microsoft 365 app reset, and BitLocker escrow verification — dry-run first, using a customer-built provisioning package and a per-device SYSTEM agent. |
| IIS and SQL Server migration | Supported | Agent-executed configuration and credential moves with preview and confirmation gates; TLS keys, TDE prerequisites, and break-glass secrets remain explicit boundary items. |
| Exchange Online mailbox content and cutover evidence | Supported | Microsoft 365 tenant-to-tenant Graph path plus certified any-to-any routes (Gmail, IMAP, EWS, archives); in-place archives and public folders migrate via the certified EWS route, with license assignment for re-guard. |
| SharePoint, OneDrive, and supported list content | Supported | Scoped Graph transfer; full app-fidelity, sharing links, and tenant governance are not implied. |
| Teams structure, membership, settings, tabs, and tags | Supported | Graph reconstruction; files and meetings move through their owning workloads. |
| Teams channel messages | Conditional | Requires Microsoft-protected-API approval and opt-in migration mode; attachments move through SharePoint and reactions are not preserved. |
| Teams private chats | Conditional | Re-creates mapped chat shells and walks full-history transport via destination OneDrive; requires secure Chat.Read.All, and history is not replayed into destination threads. |
From discovery to verification - in four operational phases.
BridgeAD standardises migration delivery so teams can assess risk early, execute in controlled waves, and close with evidence-backed reporting.
Discover
Connect source and destination environments and run read-only discovery. Baseline identity, directory, and workload readiness before scope is committed.
Plan
Build mapping rules, wave strategy, and rollback guardrails. Dry-run validates assumptions. It produces a clear execution plan per migration phase.
Execute
Execute dependency-ordered jobs with retry, resume, and real-time progress telemetry. Pause, resume, cancel, or retry failed items without losing control.
Verify & close
Run reconciliation checks and export audit and job reports. Close with governed handover and operational evidence for client, security, and compliance teams.
Built for delivery teams, not just demos.
BridgeAD includes the controls and integrations required to run migration programs at enterprise scale.
Assessment & reporting
Pre-migration readiness scoring, finding categorisation, and exportable reports in CSV, Excel, and PDF formats.
Real-time operations
SignalR live dashboards, health checks, metrics endpoints, and alert-ready telemetry for NOC and delivery teams.
API & automation
Comprehensive authenticated APIs and signed webhook notifications. Integrates with ITSM, SIEM, and internal orchestration pipelines.
On-prem execution agent
Outbound-only Windows agent with pairing, heartbeat monitoring, command dispatch, and controlled auto-update workflows.
Security Migration content is streamed, not retained by the control plane.
BridgeAD persists the operational metadata needed to orchestrate and audit work. Mail, file, and message bodies are not retained at rest in BridgeAD infrastructure.
- Customer migration content is streamed source → destination; no mailbox, file, or message body is persisted at rest in BridgeAD infrastructure.
- All Microsoft Graph and Exchange traffic is TLS 1.2+; internal control plane uses TLS termination and mutual authentication.
- Secrets are stored in Azure Key Vault (SaaS) or DPAPI-protected local stores (self-hosted). Access tokens are never logged.
- Multi-tenant deployments enforce per-tenant data isolation via Entity Framework query filters and database-level row filters.
- Five-tier RBAC (Viewer, Migration Operator, Tenant Admin, Platform Admin, Super Admin) with mandatory MFA for all privileged roles.
- Self-hosted edition keeps every byte of customer data inside the customer's own infrastructure.
Two deployment models. One orchestration approach.
Use managed SaaS or deploy the control plane in customer-managed infrastructure. Available features and required egress are confirmed during solution design.
SaaS
Multi-tenant managed service hosted on Azure. Region-pinned data residency. Per-seat or per-mailbox licensing. Fastest path to first migration.
Self-hosted
Single-tenant deployment inside the customer's Azure subscription, Kubernetes environment, or Docker host. Microsoft 365 workloads still require approved outbound access to Microsoft APIs.
Built and operated by the team you hold accountable.
BridgeAD is a product of Apqor Technologies Pvt Ltd , an engineering company based in Hyderabad, India. There is no reseller layer or outsourced support desk between you and the people who build the platform.
Direct accountability
Migration engineering, security review, and commercial questions route to the team that ships the product. The same engineers who write the orchestration review your controlled-pilot plan.
Claim discipline
Every public capability statement maps to a reviewed claim ledger and a readiness status — Supported, Conditional, Controlled pilot, or Manual. We publish boundaries next to claims rather than behind a sales call.
Deployment control
Run managed SaaS with region-pinned residency, or self-host inside your own subscription, Kubernetes cluster, or Docker host. Your compliance boundary is a first-class design input, not an afterthought.
Evidence over assurance
Assessment findings, dry runs, reconciliation, and sign-off exports are produced as verifiable artifacts. You evaluate us on what the platform records, not on what we promise.
Common questions.
Do we need an agent on every user workstation?
Not for directory or Microsoft 365 workload migrations: one healthy agent per reachable domain is often sufficient. Device-local workflows such as controlled-pilot cloud-native conversion are different. They require a healthy agent running as SYSTEM on each target Windows device for the conversion window.
Does BridgeAD store our mailbox or file content?
No. Migration content is streamed in transit from source to destination. Only metadata required for orchestration (job state, error counts, audit records) is persisted – never bodies of mail, files, or messages.
What is your Microsoft 365 workload migration readiness?
Exchange Online mailbox content (including certified any-to-any routes to and from Gmail, IMAP, on-premises Exchange, and PST/EML archives), SharePoint and OneDrive content, and Teams structure reconstruction are supported within their documented prerequisites and exclusions. Teams channel-message import is conditional on Microsoft protected-API approval. See the workload directory for exact scope and manual boundaries.
Where does our data live in the SaaS edition?
You pin a primary Azure region at provisioning. All customer-scoped data (audit log, configuration, secrets in Azure Key Vault) stays in that region. Operational telemetry may be processed in additional regions under SCC-equivalent safeguards.
Can we run BridgeAD on-prem or in our own subscription?
Yes. The self-hosted edition deploys via Helm chart, raw Kubernetes manifests, or Docker Compose, and runs entirely inside your subscription or data centre. SaaS and self-hosted ship from the same codebase.
How is access controlled?
Five-tier RBAC: Viewer, Migration Operator, Tenant Admin, Platform Admin, Super Admin. MFA is mandatory for every privileged role. All sign-ins and privilege changes are recorded to the immutable audit log.
Can BridgeAD integrate with our internal tooling?
Yes. BridgeAD exposes authenticated REST APIs and webhook notifications for job events and audit automation. Downstream integrations include ITSM, SIEM, and delivery runbooks.
Do you offer a sandbox or proof-of-concept?
Yes. Request a scoped PoC at sales[at]bridgead[dot]in with your source & destination tenant context.
Ready to plan your migration?
Tell us about your tenants and timeline. We respond within one business day.